Recognised by NASA · Hall of Fame

SOC AnalystPenetration TesterCTF DeveloperBug Bounty HunterSecurity Researcher

I build secure infrastructure and break logical flaws, from SOC operations to CTF design and bug bounty.

18
Certifications
3
Projects
NASA
Letter of Recognition
Scroll

Approach

Defensive by training.
Offensive by curiosity.

SOC operations and threat hunting on one side. CTF design, penetration testing and bug bounty on the other.

Recognition

Recognised by NASA.

Letter of Recognition and Hall of Fame for responsible vulnerability disclosure.

Certified and trained by

  • ICC2
  • Splunk
  • AWS
  • LetsDefend
  • AWS Academy
  • Cisco U
  • RED TEAM LEADERS
  • TryHackMe
  • CyberWarFare Labs
  • Hack and Fix
  • Fortinet
  • OPSWAT
  • Cisco Netacad
  • ICC2
  • Splunk
  • AWS
  • LetsDefend
  • AWS Academy
  • Cisco U
  • RED TEAM LEADERS
  • TryHackMe
  • CyberWarFare Labs
  • Hack and Fix
  • Fortinet
  • OPSWAT
  • Cisco Netacad

About

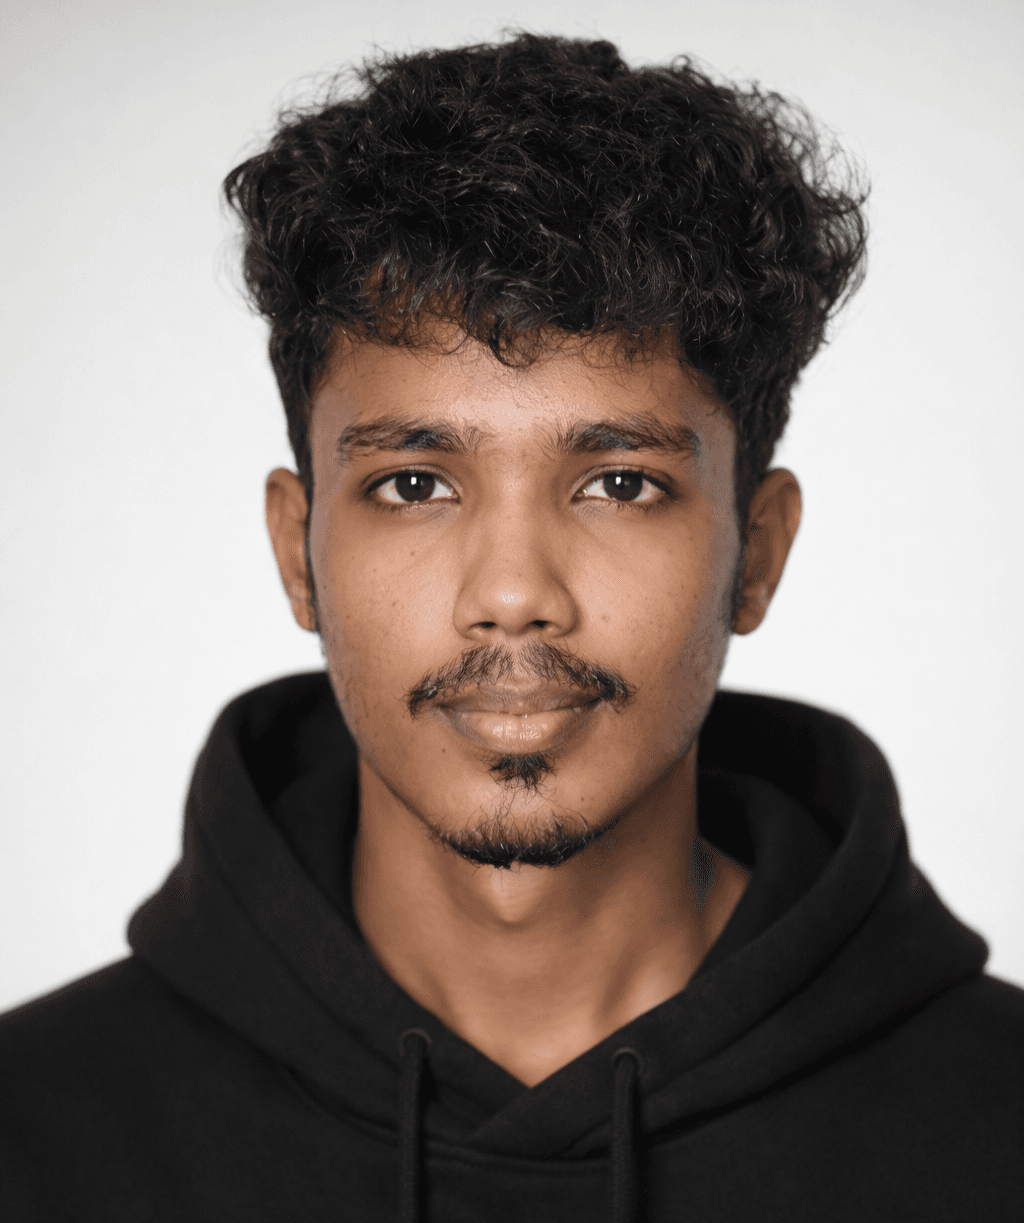
The person behind the handle.

Madhusankha Nayanajith

Madhusankha Nayanajith

0xMadhusankha · Xghost

I'm Madhusankha, a security analyst focused on defensive security, networking and CTF development.

I run a home SOC lab, write security tooling in C, design CTF challenges for other people to break, and hunt for vulnerabilities on public disclosure programmes. I'm currently a BICT undergraduate at South Eastern University of Sri Lanka.

Role
Security Analyst & CTF Developer
Education
BICT undergraduate, South Eastern University of Sri Lanka
Focus
Defensive security, network security, CTF development, bug bounty
Based in
Sri Lanka

Recognition

The bug bounty journey.

Vulnerabilities I have reported through public disclosure programmes, and the recognition that followed.

1

recognition so far,
and the hunt continues.

  1. 01
    LEARN
    Recognition

    LEARN

    Letter of Recommendation

    Reported security vulnerabilities in LEARN's systems, including its Network Operations Centre application, and worked with the LEARN team on the fixes.

    • Letter of Recommendation
    Read the letterSigned by LEARN · PDF
  2. Next recognition

    This space fills as new reports are recognised.

Projects

Built, broken and defended.

Tools I have written, labs I run and challenges I have designed.

CTF

0xArena: Operation Treasury

The Mission: Intelligence has found a secret web portal linked to a massive Treasury Bond scam. The main suspect has fled the country, but their digital footprint remains. Your Objective: You are the lead Forensic Analyst. Your job is to break into this secure portal, bypass the defences, and find the hidden evidence (The Flag) before the system deletes everything. The Challenge: The evidence is hidden using advanced encryption and stealth techniques. You must use your skills in Digital Forensics and Cryptography to uncover the truth. Evidence Verify Portal :- https://ctf.madhusankha.com/ Status: Classified Target: Secure Gateway Goal: Recover the Flag

  • DFIR
  • Cryptography
  • Steganography
  • OSINT

Skills

Where the time goes.

Blue team

  • SOC Operations
  • Threat Hunting
  • Network Security

Red team

  • Social Engineering
  • Penetration Testing

Programming

  • C Programming
  • Python Automation

Cloud and infrastructure

  • AWS Cloud Security
  • Data Center Architecture

Web development

  • Secure Web Development
  • Social Engineering
  • C Programming
  • Secure Web Development
  • SOC Operations
  • Threat Hunting
  • Penetration Testing
  • Python Automation
  • AWS Cloud Security
  • Network Security
  • Data Center Architecture
  • Social Engineering
  • C Programming
  • Secure Web Development
  • SOC Operations
  • Threat Hunting
  • Penetration Testing
  • Python Automation
  • AWS Cloud Security
  • Network Security
  • Data Center Architecture

Contact

Let's talk.

Internships, CTF collaborations, security work or a question about one of the projects. Email is the fastest way to reach me.

madhusankanayanajith@gmail.com

Find me on